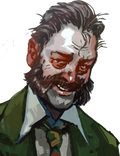
Hard Pass
  • Communities
  • Create Post
  • Create Community
  • heart
    Support Lemmy
  • search
    Search
  • Login
  • Sign Up
night_petal@lemmy.zip to Lemmy Shitpost@lemmy.world · 10 hours ago

My Private Key

lemmy.zip

external-link
message-square
30
link
fedilink
  • cross-posted to:
  • programmer_humor@programming.dev
308
external-link

My Private Key

lemmy.zip

night_petal@lemmy.zip to Lemmy Shitpost@lemmy.world · 10 hours ago
message-square
30
link
fedilink
  • cross-posted to:
  • programmer_humor@programming.dev
alert-triangle
You must log in or register to comment.
  • someone@lemmy.today
    link
    fedilink
    arrow-up
    1
    ·
    2 hours ago

    Wait a minute… There’s something bothering me about this place…

  • weps@lemmy.world
    link
    fedilink
    arrow-up
    3
    ·
    4 hours ago

    I’m using PHP 4

    is that what this is about

    • weps@lemmy.world
      link
      fedilink
      arrow-up
      2
      ·
      4 hours ago

      all the fuss

  • MinnesotaGoddam@lemmy.world
    link
    fedilink
    English
    arrow-up
    1
    ·
    3 hours ago

  • TheLeadenSea@sh.itjust.works
    link
    fedilink
    English
    arrow-up
    27
    ·
    10 hours ago

    What’s this a reference to?

    • Rentlar@lemmy.ca
      link
      fedilink
      arrow-up
      85
      arrow-down
      1
      ·
      10 hours ago

      https://www.theregister.com/security/2026/10/20/indian-certification-authority-emudhras-private-keys-compromised-one-of-them-was-the-number-4/5304312

      It was discovered that one of India’s Trusted Certificate Authorities, eMudhra, tasked with signing website certificates to verify authenticity of HTTP traffic was using the number “4” as the signing key along with 7 other keys less than 250. The key is supposed to be a unique number hundreds of binary digits long, but with such a simple key anybody can spoof a certificate that they could claim was signed by eMudhra and CA-checking lists would accept that.

      • danc4498@lemmy.world
        link
        fedilink
        English
        arrow-up
        4
        ·
        3 hours ago

        At least use a GUID generator website to generate it like the rest of us.

      • MrSelfDestruct@quokk.au
        link
        fedilink
        English
        arrow-up
        5
        arrow-down
        31
        ·
        9 hours ago

        Nerd alert!

        • danc4498@lemmy.world
          link
          fedilink
          English
          arrow-up
          3
          ·
          3 hours ago

          You got a lot of downvote for this, lol.

    • adr1an@programming.dev
      link
      fedilink
      arrow-up
      48
      ·
      9 hours ago

      4 has been breached. Update your browsers! We are using 5 now :)

      • krashmo@lemmy.world
        link
        fedilink
        arrow-up
        23
        ·
        9 hours ago

        I’m using 8. It’s twice as secure

        • MsPenguinette@lemmy.world
          link
          fedilink
          arrow-up
          5
          ·
          4 hours ago

          We can’t afford the computational overhead of 8! Help plz

    • night_petal@lemmy.zipOP
      link
      fedilink
      arrow-up
      23
      arrow-down
      1
      ·
      edit-2
      10 hours ago

      How do I begin? Basically, an India based company that does TLS certification published some comically bad private keys. One of which was just the character 4. Update all of your browsers btw, desktop and mobile. This is a very major low level security breech of the entire internet.

      It may take Linux distros days to patch it, and this includes millions of servers.

    • virku@lemmy.world
      link
      fedilink
      arrow-up
      20
      ·
      10 hours ago

      An ssl certificate provider used 4 as their private key. This should be hundreds of characters long. Somebody figured this out and was able to issue their own certificates based on it. This results in loss of trust in their certificates which is a big deal.

      It is compared as bigger than one of the largest security issues in IT the last couple of years since it forces everybody to patch their shit to not trust this certificate chain. And lots of stuff aren’t patched that easily.

      • Hawke@lemmy.world
        link
        fedilink
        arrow-up
        11
        ·
        10 hours ago

        I bet they used 0000000000…004

        See, hundreds of digits long!

        • prettybunnys@piefed.social
          link
          fedilink
          English
          arrow-up
          8
          arrow-down
          1
          ·
          9 hours ago

          I mean …. Yes, that would be secure.

          Sorta.

          It’s be dumb, and a pattern based attack could potentially solve it easily … but technically much more secure than 4

          • sirprize@discuss.tchncs.de
            link
            fedilink
            arrow-up
            1
            ·
            3 hours ago

            I get what you mean, but no, it would not be secure. The private key in question is really used as a number in a calculation, not as a string of digits. Leading zeroes would just be ignored.

            • prettybunnys@piefed.social
              link
              fedilink
              English
              arrow-up
              1
              ·
              3 hours ago

              not when it’s a representation of bits in a file

              The key itself being 00000000004 yah

              The key file being

              0000000000000000000000……4 is a different story

    • SpaceNoodle@lemmy.world
      link
      fedilink
      arrow-up
      12
      ·
      10 hours ago

      4

    • OptimusPrimeDownfall@discuss.tchncs.de
      link
      fedilink
      English
      arrow-up
      11
      ·
      10 hours ago

      eMudhra, an Indian tech firm, had a root TLS cert with laughably low size for one of its encryption keys https://scotthelme.co.uk/eight-bits-of-trust-emudhras-ca-keys-cracked-in-milliseconds/

    • rockSlayer@lemmy.blahaj.zone
      link
      fedilink
      English
      arrow-up
      8
      ·
      10 hours ago

      A company from India was issuing Internet security certificates with extremely small private keys. The lowest they issued was 4

  • the_beber@feddit.org
    link
    fedilink
    arrow-up
    14
    ·
    10 hours ago

    Reminds me of the scene in Space Balls, where the passcode to a planet‘s atmosphere protection is revealed to the villan amd it‘s just 1234. … except this is arguably worse.

    • ironhydroxide@sh.itjust.works
      link
      fedilink
      English
      arrow-up
      9
      ·
      9 hours ago

      Wasn’t it 12345? And the same code as the president’s luggage?

      • obviouspornalt@fedinsfw.app
        link
        fedilink
        English
        arrow-up
        1
        ·
        5 hours ago

        altr

      • running_ragged@lemmy.world
        link
        fedilink
        English
        arrow-up
        6
        ·
        9 hours ago

        No, it was 4. The same as the nuclear code.

      • the_beber@feddit.org
        link
        fedilink
        arrow-up
        2
        ·
        7 hours ago

        Yes it was 12345 in the movie. I forgor… so maybe it is safe.

    • night_petal@lemmy.zipOP
      link
      fedilink
      arrow-up
      4
      ·
      10 hours ago

      The entire world’s data VS the entire world’s air.

  • epochreachers@lemmy.blahaj.zone
    link
    fedilink
    arrow-up
    3
    ·
    8 hours ago

    Four, four, four, four, four

    Skate

    Four

    Skate

    (Look I got the reference)

  • czer0@sh.itjust.works
    link
    fedilink
    arrow-up
    2
    ·
    7 hours ago

    I’m using 11111

  • Envidon@feddit.nl
    link
    fedilink
    arrow-up
    3
    ·
    9 hours ago

    Ironically all the numbers in this meme would’ve made for a better private key.

Lemmy Shitpost@lemmy.world

lemmyshitpost@lemmy.world

Subscribe from Remote Instance

Create a post
You are not logged in. However you can subscribe from another Fediverse account, for example Lemmy or Mastodon. To do this, paste the following into the search field of your instance: !lemmyshitpost@lemmy.world

Welcome to Lemmy Shitpost. Here you can shitpost to your hearts content.

Anything and everything goes. Memes, Jokes, Vents and Banter. Though we still have to comply with lemmy.world instance rules. So behave!


Rules:

1. Be Respectful

Refrain from using harmful language pertaining to a protected characteristic: e.g. race, gender, sexuality, disability or religion.

Refrain from being argumentative when responding or commenting to posts/replies. Personal attacks are not welcome here.

…


2. No Illegal Content

Content that violates the law. Any post/comment found to be in breach of common law will be removed and given to the authorities if required.

That means:

-No promoting violence/threats against any individuals

-No CSA content or Revenge Porn

-No sharing private/personal information (Doxxing)

…


3. No Spam

Posting the same post, no matter the intent is against the rules.

-If you have posted content, please refrain from re-posting said content within this community.

-Do not spam posts with intent to harass, annoy, bully, advertise, scam or harm this community.

-No posting Scams/Advertisements/Phishing Links/IP Grabbers

-No Bots, Bots will be banned from the community.

…


4. No Porn/Explicit

Content


-Do not post explicit content. Lemmy.World is not the instance for NSFW content.

-Do not post Gore or Shock Content.

…


5. No Enciting Harassment,

Brigading, Doxxing or Witch Hunts


-Do not Brigade other Communities

-No calls to action against other communities/users within Lemmy or outside of Lemmy.

-No Witch Hunts against users/communities.

-No content that harasses members within or outside of the community.

…


6. NSFW should be behind NSFW tags.

-Content that is NSFW should be behind NSFW tags.

-Content that might be distressing should be kept behind NSFW tags.

…

If you see content that is a breach of the rules, please flag and report the comment and a moderator will take action where they can.


Also check out:

Partnered Communities:

1.Memes

2.Lemmy Review

3.Mildly Infuriating

4.Lemmy Be Wholesome

5.No Stupid Questions

6.You Should Know

7.Comedy Heaven

8.Credible Defense

9.Ten Forward

10.LinuxMemes (Linux themed memes)


Reach out to

All communities included on the sidebar are to be made in compliance with the instance rules. Striker

Visibility: Public
globe

This community can be federated to other instances and be posted/commented in by their users.

  • 3.81K users / day
  • 8.62K users / week
  • 14.5K users / month
  • 27.8K users / 6 months
  • 1 local subscriber
  • 42.4K subscribers
  • 19.9K Posts
  • 329K Comments
  • Modlog
  • mods:
  • Aer@lemmy.world
  • WiildFiire@lemmy.world
  • Decoy321@lemmy.world
  • The Picard Maneuver@startrek.website
  • Flying Squid@lemmy.world
  • The Picard Maneuver@lemmy.world
  • BE: 0.19.20
  • Modlog
  • Legal
  • Instances
  • Docs
  • Code
  • join-lemmy.org